- When
- America/Chicago (CST)
- Where
- NTEKNO™ SecureStack™ Training | Granite Place at Southlake Town Square550 Reserve Street Suite 190, Southlake, TX 76092
Tickets are sold on Eventbrite. We link straight to the listing — nothing is bought here. Listing details come from the source and can change. Eventovia indexes events; it does not organize them or sell tickets. Terms & Disclaimer
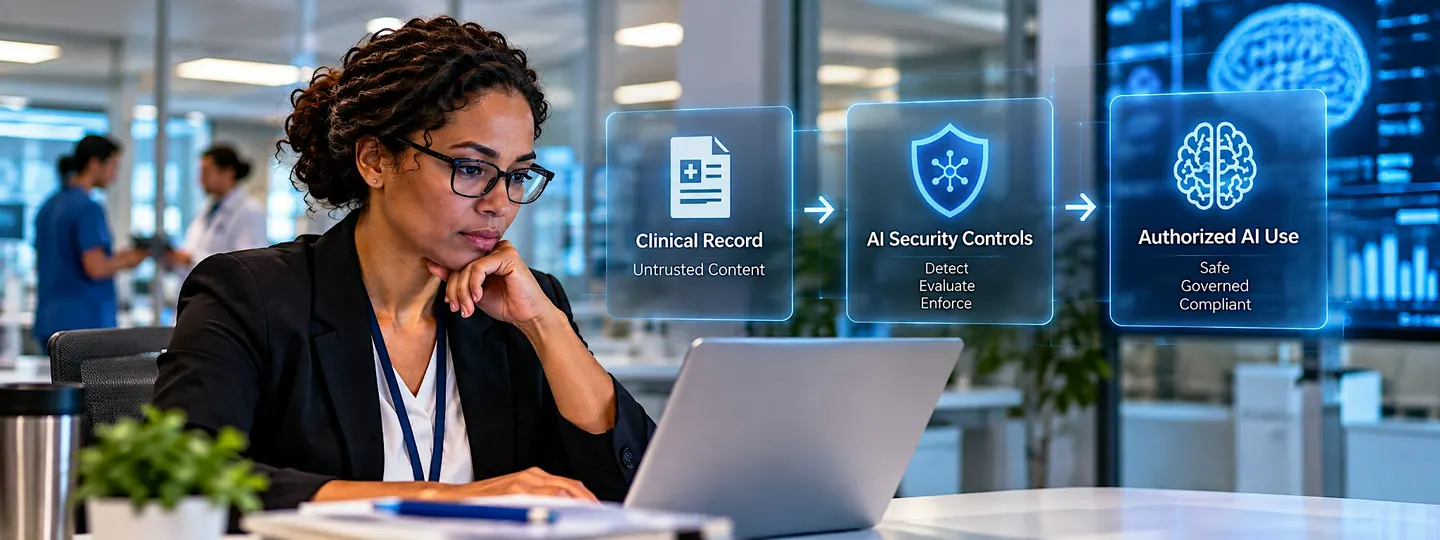
Securing AI in Healthcare: Prompt Injection to Unauthorized Actions takes place on Tue, Jan 12, 2027 at 9:00 AM (CST) at NTEKNO™ SecureStack™ Training | Granite Place at Southlake Town Square in Denton, TX. Tickets are $700 + on Eventbrite.
About this event
An instructor leads security training on prompt injection and validation in healthcare AI.
Full description from organizerShow less
Instructor-led security training on prompt injection, authorization boundaries, and evidence-based validation in healthcare AI workflows. What happens when an AI-enabled healthcare application encounters malicious instructions hidden inside a clinical record? Can the application detect those instructions before the AI model processes the record? And if an AI-enabled workload attempts an unnecessary operation, will its Azure permissions prevent that action? Securing AI in Healthcare: Prompt Injection to Unauthorized Actions is a one-day, in-person instructor-led course designed to investigate these questions through hands-on Microsoft Azure security exercises. Participants examine two critical security boundaries: • Content Boundary: How malicious instructions embedded in untrusted clinical content are detected, and how application logic enforces the security decision before model invocation. • Authorization Boundary: How workload permissions govern access to Azure resources, and how controlled READ and WRITE operations provide observable evidence of permitted and restricted actions. Through two structured labs, participants move beyond discussing AI security risks to examining what the implemented controls actually demonstrate. The objective is not simply to understand the threat. It is to test the security boundary, observe the result, and defend the conclusion with technical evidence. Tuesday, January 12, 2027, 9:00 AM–5:00 PM CST Class size is limited to 10 participants to preserve the hands-on experience. What you'll investigate The training follows two related security boundaries. Prompt injection and application enforcement Examine a healthcare AI workflow in which externally sourced clinical content contains an adversarial instruction. Use Azure AI Content Safety Prompt Shields to evaluate the content and examine how application logic enforces the security decision before model invocation. Authorization boundaries and unnecessary actions Examine what an AI-enabled workflow is authorized to do compared with what the business operation actually requires. Evaluate READ versus WRITE requirements and use observable execution evidence to support conclusions about whether access is appropriately constrained. Hands-on training environment No Azure subscription is required from participants during the training. Each participant will be assigned an Azure resource group for the hands-on exercises. Microsoft Azure & AI Security Technologies Used in the Hands-On Labs • Azure AI Content Safety Prompt Shields • Azure Blob Storage • Azure Functions • Azure Logic Apps • Azure Role-Based Access Control (Azure RBAC) What you'll practice • Identifying indirect prompt-injection risk in healthcare AI workflows. • Validating Prompt Shields detection results. • Examining application enforcement before model invocation. • Evaluating authorization requirements against the intended business operation. • Distinguishing required READ access from unnecessary WRITE capability. • Using observable technical evidence instead of assumptions to support security conclusions. What you walk away with • Hands-on experience examining two AI application security boundaries. • A practical approach for validating security controls through observable evidence. • Experience connecting prompt-injection detection, application enforcement, and authorization decisions. • A framework for communicating defensible technical conclusions about AI security risk. • An NTEKNO Certificate of Completion documenting the training and instructional time. Professional development documentation • The training documents 370 minutes (6 hours 10 minutes) of instructional and hands-on lab time. • Participants receive an NTEKNO Certificate of Completion and may submit their training documentation to their credentialing organization for consideration. • CPE or CEU eligibility and any credit awarded are determined by the applicable credentialing organization. Your instructor Serling A. Davis Founder & Chief Learning Architect, NTEKNO, Inc. Serling A. Davis is a cloud security and technical education professional with 20 years of experience developing and delivering advanced technical training across cybersecurity, cloud infrastructure, telecommunications, and enterprise technologies. Before founding NTEKNO, Serling served as Principal Content Developer within Microsoft Worldwide Learning's Security, Compliance & Identity organization. He was the principal content developer and global portfolio custodian for AZ-500: Microsoft Azure Security Technologies, responsible for curriculum quality, technical accuracy, practitioner alignment, and continuous program improvement. He also developed the SC-5002 Applied Skills learning path, including GitHub-based technical labs, assessments, validation guidance, and supporting instructional resources. His career includes technical instructor and curriculum development positions with Palo Alto Networks, Ericsson, Huawei Technologies, Imperva, and Alcatel. His instructional experience spans optical networking, 2G, 3G, 4G LTE and 5G infrastructure, network virtualization, cloud orchestration, and cloud-native security. Throughout his career, Serling has developed technical training content and delivered instructor-led education for organizations including Verizon Wireless, Vodafone Germany, Swisscom AG, Spark New Zealand, TELUS Canada, Orange SA, China Telecom Hong Kong, Tata Communications Canada, Level 3 Communications, Sprint Corporation, Santee Cooper Power, and the Metropolitan Atlanta Rapid Transit Authority (MARTA). As Founder and Chief Learning Architect of NTEKNO, Inc., Serling created SecureStack™, a scenario-based cloud and AI security training portfolio incorporating Microsoft technologies such as Defender for Cloud, Sentinel, Purview, Security Copilot, Copilot in Azure, and Azure AI Content Safety Prompt Shields. His instructional approach emphasizes a central principle: security conclusions must be supported by what technology demonstrably detects, enforces, authorizes, and records—not by assumption. For Securing AI in Healthcare: Prompt Injection to Unauthorized Actions, Serling applies this methodology through hands-on instruction examining indirect prompt injection, application-layer enforcement, authorization boundaries, and observable technical evidence. Full course details and registration View the complete course details and register directly with NTEKNO. View course details and registration Why NTEKNO SecureStack™? Security training should demonstrate what works—not simply explain how technology is supposed to work. NTEKNO SecureStack™ delivers scenario-based, instructor-led training built around realistic security investigations, hands-on technical exercises, and observable evidence. Led by a former Microsoft Worldwide Learning Principal Content Developer, this course emphasizes the practical distinction between detecting a security threat, enforcing an application-level control, and validating authorization boundaries. Participants work through structured exercises designed to strengthen technical judgment and support defensible security decisions. Registration, Cancellation & Refund Information Registration: Advance registration is required.
Keep going
All Denton events →Similar events
View all →

Details
- When
- Tue, Jan 12, 2027 · 9:00 AM (CST)
- Where
- NTEKNO™ SecureStack™ Training | Granite Place at Southlake Town Square
- Address
- 550 Reserve Street Suite 190, Southlake, TX 76092
- Price
- $700 +
- Genre
- Panel & Seminar
Questions
- When is Securing AI in Healthcare: Prompt Injection to Unauthorized Actions?
- Tue, Jan 12, 2027 at 9:00 AM CST.
- How much are tickets for Securing AI in Healthcare: Prompt Injection to Unauthorized Actions?
- Tickets are $700 +.
- Where is Securing AI in Healthcare: Prompt Injection to Unauthorized Actions?
- NTEKNO™ SecureStack™ Training | Granite Place at Southlake Town Square, 550 Reserve Street Suite 190, Southlake, TX 76092, Denton, TX.
- Where can I buy tickets for Securing AI in Healthcare: Prompt Injection to Unauthorized Actions?
- Tickets are sold on Eventbrite. This page links straight to that listing; no tickets are sold here.