- When
- America/Chicago (CST)
- Where
- I2C850 Ben Graves Drive, Huntsville, AL 35899
Tickets are sold on Eventbrite. We link straight to the listing — nothing is bought here. Listing details come from the source and can change. Eventovia indexes events; it does not organize them or sell tickets. Terms & Disclaimer
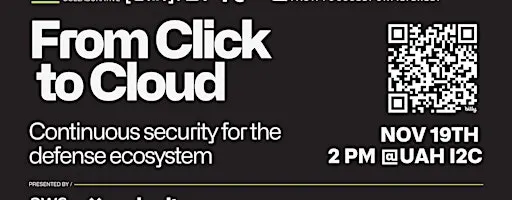
ARC X CTX : FROM CLICK TO CLOUD : CONTINUOUS CYBER DEFENSE takes place on Thu, Nov 19, 2026 at 2:00 PM (CST) at I2C in Huntsville, AL. Entry is free; the listing is on Eventbrite.
About this event
From Click to Cloud unites AWS, Palo Alto Networks, and UAH CCRE to explore continuous cyber defense, Zero Trust, and resilience.
Full description from organizerShow less
From Click to Cloud unites AWS, Palo Alto Networks, and UAH CCRE to explore continuous cyber defense, Zero Trust, and resilience. From Click to Cloud: Continuous Cyber Defense ARC Hyperconference Series / HIGH SIGNAL. ZERO FLUFF. Presented by ARC, CTX and UAH I²C , in collaboration with AWS, Palo Alto Networks and UAH CCRE EVENT OVERVIEW The threat environment does not operate on an assessment schedule. Security cannot either. From Click to Cloud: Continuous Cyber Defense is a fast-paced Hyper-conference examining how organizations can move beyond point-in-time compliance and build security practices that continuously protect users, endpoints, infrastructure, data and mission-critical systems. This education-first program brings together the complementary perspectives of AWS, Palo Alto Networks and UAH’s Center for Cybersecurity Research and Education—CCRE. Through two focused talks and two practitioner panels, participants will explore the human, architectural and operational dimensions of modern cyber defense. The program will address four critical questions: • How should organizations translate NIST SP 800-171 requirements into practical readiness priorities? • Where do human behavior, identity and endpoint controls create hidden security gaps? • What does Zero Trust look like as an operating architecture—not merely a policy objective? • How can organizations navigate the path from security scans and evidence to authorization and continuous monitoring? The conference is designed for leaders and practitioners who want substantive, actionable discussion—not another high-level compliance briefing or extended product presentation. -------------- WHO SHOULD ATTEND? This program is designed for professionals across the defense industrial base, federal contracting community, government, academia and the broader technology ecosystem, including: • Business owners and executive leaders • CISOs, CIOs and cybersecurity leaders • Government and defense contractors • Information technology and cloud teams • Security engineers and architects • Compliance, risk and governance professionals • Program managers and contracting professionals • Organizations navigating NIST SP 800-171, CMMC or ATO requirements • Managed security and technology service providers • Researchers, faculty and students working in cybersecurity -------------- PROGRAM AGENDA 2:00–2:10 pm: Welcome and Conference Framing 2:10–2:55 pm: Session 1 — Panel: The NIST SP 800-171 Readiness Guide A practical conversation about turning NIST SP 800-171 requirements into an actionable security program. Panelists will examine readiness, scoping, evidence, common control gaps and the difference between documenting a security practice and demonstrating that it works consistently. Topics will include: • Understanding the operational intent behind NIST SP 800-171 • Identifying systems, users and data within scope • Recognizing common readiness and evidence gaps • Connecting technical controls to policies and operational practices • Moving from periodic preparation to continuous monitoring • Prioritizing improvements when time and resources are limited 2:55–3:40 pm: Session 2 — Talk: Closing the “Human-in-the-Loop” Gap Technology can strengthen security, but people, identities and endpoints remain central to the attack surface. This session will explore how organizations can reduce human-layer risk without creating unnecessary friction for employees, administrators and partners. Topics will include: • Identity, authentication and least-privilege access • Endpoint posture and behavioral visibility • Remote users and distributed work environments • Phishing, social engineering and credential compromise • Privileged access and administrative separation • Data-loss prevention and unauthorized data movement • Connecting user and endpoint telemetry to continuous detection 3:40–3:50 pm: Networking Break 3:50–4:35 pm: Session 3 — Talk: Zero Trust: The Architecture Behind the Requirements Zero Trust is frequently discussed as a principle. This session will examine what it means as an operating architecture across users, applications, workloads, networks and data. Topics will include: • Translating Zero Trust principles into architecture • Identity-centered access and authorization • Protecting cloud applications, workloads and storage • Segmentation and reducing unnecessary exposure • Encryption, key management and private connectivity • Logging, telemetry and continuous visibility • Shared responsibility across cloud providers and customers • Building security controls that support both mission and compliance objectives 4:35–5:20 pm: Session 4 — Panel: The ATO Gauntlet: From Scan to Signature What happens between identifying a security requirement and receiving authorization to operate? This practitioner panel will examine the technical, evidentiary and organizational challenges that arise along the authorization journey—and why successful authorization depends on more than passing a scan. Topics will include: • Preparing systems and teams for the authorization process • Vulnerability scans, findings and remediation decisions • Security documentation and defensible evidence • POA&Ms, risk acceptance and control ownership • Coordination among technical, compliance and mission teams • Common causes of delay and rework • Maintaining the security posture after authorization • Connecting continuous monitoring to ongoing risk decisions 5:20–5:30 pm: Closing Actions and Key Takeaways A concise summary of the most important actions organizations can take to strengthen readiness, visibility and resilience. 5:30–7:30 p.m. Networking Reception and Drinks Continue the conversation with speakers, cybersecurity practitioners, researchers and technology leaders from across the Huntsville ecosystem. The reception will provide space for deeper technical discussions, partner conversations and new connections across industry, government and academia. -------------- WHAT YOU WILL TAKE AWAY Attendees will leave with: • A clearer understanding of NIST SP 800-171 readiness priorities • Practical insight into human, identity and endpoint security gaps • A stronger view of Zero Trust as an end-to-end architecture • Greater awareness of the technical and evidentiary demands of the ATO process • Actionable ideas for strengthening continuous monitoring • New connections across Huntsville’s cybersecurity ecosystem -------------- ABOUT THE HYPER-CONFERENCE SERIES The Hyperconference Series is built around concentrated programming, substantive conversations, and practical insight. Each event brings together leaders from industry, academia and government to examine a complex technology challenge from multiple perspectives—without the filler of a traditional all-day conference. High signal. Zero fluff. -------------- HOST AND PROGRAM PARTNERS UAH Invention to Innovation Center—I²C / ARC / CTX Conference convener, ecosystem engagement and program framing Amazon Web Services—AWS Zero Trust, cloud architecture, data protection and continuous monitoring Palo Alto Networks Human-layer, identity, endpoint, network and continuous-threat visibility UAH Center for Cybersecurity Research and Education—CCRE Cybersecurity research, education, NIST readiness and authorization perspectives -------------- RESERVE YOUR SEAT Join cybersecurity, technology and defense-sector leaders for an intensive afternoon focused on protecting the entire digital pathway—from the first user click to the cloud systems supporting the mission. Capacity is limited. Register today. -------------- Program and participating speakers are subject to change. This event is educational and does not constitute a certification assessment, compliance determination or guarantee of an authorization to operate.
Keep going
All Huntsville events →Similar events
View all →

Details
- When
- Thu, Nov 19, 2026 · 2:00 PM (CST)
- Where
- I2C
- Address
- 850 Ben Graves Drive, Huntsville, AL 35899
- Price
- Free
- Genre
- Panel & Seminar
Questions
- When is ARC X CTX : FROM CLICK TO CLOUD : CONTINUOUS CYBER DEFENSE?
- Thu, Nov 19, 2026 at 2:00 PM CST.
- How much are tickets for ARC X CTX : FROM CLICK TO CLOUD : CONTINUOUS CYBER DEFENSE?
- Entry is free.
- Where is ARC X CTX : FROM CLICK TO CLOUD : CONTINUOUS CYBER DEFENSE?
- I2C, 850 Ben Graves Drive, Huntsville, AL 35899, Huntsville, AL.
- Where can I buy tickets for ARC X CTX : FROM CLICK TO CLOUD : CONTINUOUS CYBER DEFENSE?
- Tickets are sold on Eventbrite. This page links straight to that listing; no tickets are sold here.