LASCON 2026 Training
- When
- America/Chicago (CDT)
- Where
- Norris Conference Centers - Austin2525 West Anderson Lane #365, Austin, TX 78757
Tickets are sold on Eventbrite. We link straight to the listing — nothing is bought here. Listing details come from the source and can change. Eventovia indexes events; it does not organize them or sell tickets. Terms & Disclaimer
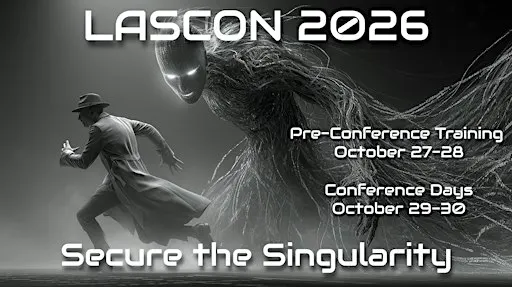
LASCON 2026 Training takes place on Tue, Oct 27, 2026 at 8:00 AM (CDT) at Norris Conference Centers - Austin in Austin, TX. Tickets are $316.63 + on Eventbrite.
About this event
The OWASP-affiliated LASCON (Lone Star Application Conference) in Austin, TX features training events focused on application security. Attendees engage in workshops and discussions led by industry experts, gaining insights into best practices and emerging trends in the field.
Full description from organizerShow less
Training events hosted along with the OWASP-affiliated LASCON (Lone Star Application Conference) in Austin, TX. L ASCON Trainings are events held in conjunction with the LASCON conference. Trainers are highly respected and experts in their field. Typically, the trainers have presented at several other quality events unrelated to OWASP, like Black Hat or other industry events. For LASCON 2025, the training offerings are both two day and one day trainings - please check the training you are signing up for the length. Offering #1: (1-Day Event, Tuesday Only) Words as Weapons: Hands-On Attacks and Defenses for LLM, RAG, and Agentic AI Systems Trainer: Pavan Reddy Abstract: Modern AI systems do not usually fail like traditional software. They often fail through language: a malicious prompt, a poisoned document, a hidden instruction, an overprivileged tool call, or an output that quietly leaks sensitive data. But despite the novelty of AI, these systems are still software. They have trust boundaries, inputs, outputs, privileges, data flows, logs, and failure modes that can be threat modeled and secured. This full-day, hands-on training teaches attendees how to break and defend realistic AI applications in a safe sandbox environment. The training focuses on LLM applications, RAG systems, AI assistants with database/tool access, prompt injection, indirect prompt injection, data exfiltration, output validation, access control, cross-tenant leakage, and practical governance. The course is designed around realistic mock systems rather than slides alone. Attendees will attack a sandboxed car dealership AI assistant connected to a database, reproduce prompt injection and tool-abuse scenarios, use red-team tooling against models, exploit indirect prompt injection patterns inspired by real-world vulnerabilities such as EchoLeak, and analyze RAG failure modes involving hidden instructions, retrieval abuse, and sensitive data exposure. No coding is required. Attendees will use prepared notebooks and browser-based labs where they can adjust attack parameters, run controlled experiments, inspect results, and understand which defenses work in practice. Each module follows the same structure: hands-on attack first, then defense implementation, then a theory recap that maps the exercise back to application security principles. By the end of the training, attendees will leave with notes for each section, a practical AI security checklist, and a boundary-based control matrix mapped to NIST 800-53-style controls. The checklist explains what each control means in an AI system, what implementation pattern satisfies it, and which scenario it applies to best. Trainers Bio: Pavan Reddy AI Researcher and Engineer Pavan Reddy is principal developer at Automata LLC, leading FIPS 140-3, FedRAMP ATO, and AI security initiatives. He is an independent AI security researcher and educator focused on making secure AI accessible at scale. He founded QBTrain, a free platform for hands-on AI and AI security education. His peer-reviewed work, published at AAAI, ACM, FLAIRS, HCII, ACSAC, and NeurIPS, spans adversarial ML, prompt injection, and foundation model vulnerabilities. He has delivered 25+ talks and workshops at BSides, OWASP, SquadCon, CAPWIC, ACM SIGCITE, NeurIPS Education, and FLAIRS, with upcoming sessions at CVPR 2026 and TechMentor at Microsoft HQ. He educates 80,000+ followers online and holds an MS in CS from George Washington University. Offering #2: (2-Day Event) Secure Coding Bootcamp: Mastering the OWASP Top 10:2026 Trainer: Rico Komenda Abstract: This intensive 2-day secure coding training immerses participants in the mindset of both attacker and defender, using a purpose-built vulnerable web application developed specifically for this course. The application reflects realistic development patterns and serves as a hands-on environment to explore, exploit, and ultimately fix security flaws commonly found in modern web applications. The training is based on the OWASP Top 10 Web 2025 and is structured as a continuous, experience-driven journey through today’s most critical risks. Each topic follows a consistent and practical approach: participants first get familiar with the vulnerability and its real-world impact through concrete examples and breach scenarios, then actively exploit the issue themselves in a guided hands-on lab, and finally work through effective mitigation strategies and secure coding techniques. This progression, from understanding risks, to attacking them, to see the mitigations, ensures that participants not only recognize vulnerabilities but also truly understand how they emerge and how to prevent them in their own codebases. While the training primarily uses Java-based examples to demonstrate secure implementation patterns, all concepts and techniques are explained in a language-agnostic way, making them applicable across a wide range of modern technology stacks. The workshop covers common areas such as input validation, authentication and session management, access control, and secure handling of data within API-driven applications. By working through realistic attack and defense scenarios, participants develop a deeper, practical understanding of secure coding. The goal is to move beyond theory and enable developers and security professionals to integrate security thinking directly into their daily development workflow. Trainers Bio: Rico Komenda Senior Security Consultant Rico is a senior security consultant at adesso SE. His main security areas are in application security, cloud security, offensive security and AI security. For him, general security intelligence in various aspects is a top priority. Today’s security world is constantly changing and you should always familiarize yourself with the most up-and-coming technologies and methodologies. As a husband and father of two, he enjoys spending time with his family and exploring the world with them. Offering #3: (2 Day Event) AI SecureOps: Attacking & Defending AI Applications and Services (2026 Edition) Trainer: Abhinav Singh Abstract: Can prompt injections lead to complete infrastructure takeovers? Could AI agents, MCP-connected tools, or poisoned external context be abused to compromise backend services? Can data poisoning in AI copilots impact a company’s stock? Can jailbreaks create false crisis alerts in security systems? This immersive, CTF-styled training in GenAI, LLM, agent, and MCP security dives into these pressing questions. Engage in realistic attack-and-defense scenarios focused on real-world threats, from prompt injection and remote code execution to backend compromise, tool abuse, unsafe agent orchestration, trust and authorization failures. Tackle hands-on challenges with live AI applications to understand vulnerabilities and build robust defenses. Learn how to build a comprehensive security pipeline, master AI red and blue team strategies, secure tool-connected and agentic systems, implement resilient guardrails for LLMs, and handle incident response for AI-based threats.
Keep going
All Austin events →Similar events
View all →



Details
- When
- Tue, Oct 27, 2026 · 8:00 AM (CDT)
- Where
- Norris Conference Centers - Austin
- Address
- 2525 West Anderson Lane #365, Austin, TX 78757
- Price
- $316.63 +
- Genre
- 102/class, training, or workshop
Questions
- When is LASCON 2026 Training?
- Tue, Oct 27, 2026 at 8:00 AM CDT.
- How much are tickets for LASCON 2026 Training?
- Tickets are $316.63 +.
- Where is LASCON 2026 Training?
- Norris Conference Centers - Austin, 2525 West Anderson Lane #365, Austin, TX 78757, Austin, TX.
- Where can I buy tickets for LASCON 2026 Training?
- Tickets are sold on Eventbrite. This page links straight to that listing; no tickets are sold here.